NSANet Went Down Nov. 17 With 'Routine Maintenance' as the Only Cause on Record
Security / news
NSANet Went Down Nov. 17 With 'Routine Maintenance' as the Only Cause on Record
Officials from the White House to the Senate Intelligence Committee say they see no attack, but the NSA has not said which systems failed or for how long.
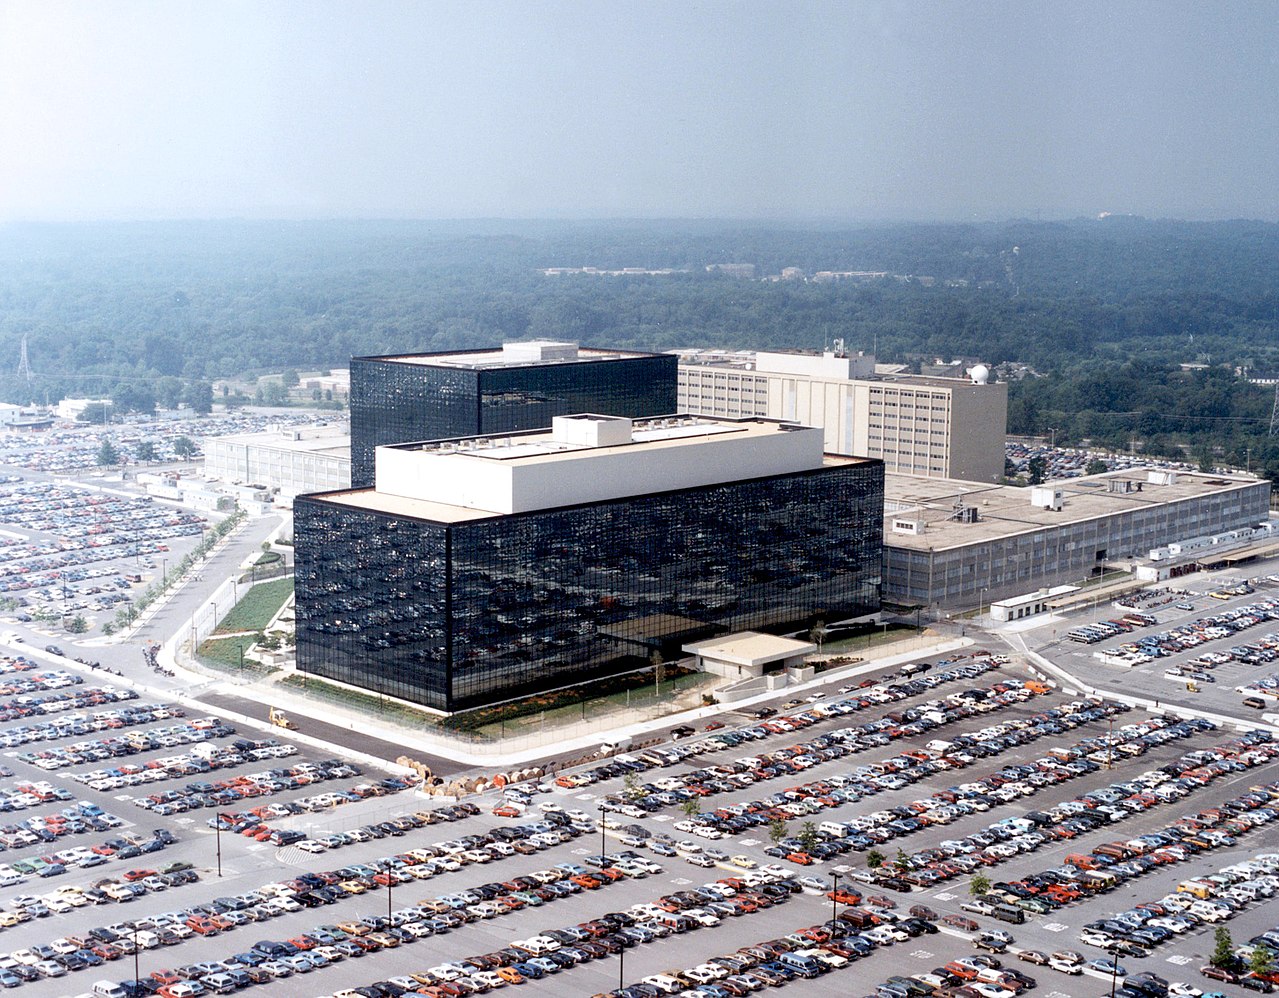
The National Security Agency's classified internal network, NSANet, went down on Nov. 17. The agency blamed routine maintenance, and the White House, the Secretary of State, the Director of National Intelligence and the Senate Intelligence Committee's top Democrat each said they saw no sign of an attack. Nobody has said what failed, or for how long.
CNN first reported the outage; the Associated Press and International Business Times, which cites CNN, carried the details used here. The only cause on the record so far is a maintenance explanation from the agency itself.
What the agency and officials have said
In a statement relayed by the AP, the NSA called the outage a "temporary degradation during scheduled routine maintenance" and said "mission-critical capabilities remain fully operational." It gave no further detail on cause or scope, and the AP quotes no named spokesperson.
A defense official, whom the AP did not name, said the problem disrupted NSANet operations. CNN reported, per IBTimes, that the outage led to staggered arrival times for personnel and that its cause, duration and extent remained unclear.
| Who | What they said | Outlet |
|---|---|---|
| NSA (statement) | "Temporary degradation during scheduled routine maintenance" | AP |
| Marco Rubio, Secretary of State and national security adviser | "Zero evidence" of hackers or hostile actors behind these incidents | AP |
| Jay Clayton, Director of National Intelligence | "Many people are patching their systems" | AP |
| Sen. Mark Warner, Senate Intelligence Committee vice chairman | Evidence points to "legitimate efforts to secure our systems, not malicious activity" | AP |
| Lauren Bis, White House spokesperson | "We see no evidence that this was a cyberattack" | IBTimes, on Newsmax |
Rubio, speaking while travelling with the president in Asia, called the reports "unsettling," the AP says. Bis added on Newsmax that "there is no crisis, or anything like that, for Americans to be worried about."
Continuity, and a run of other failures
CNN reported that urgent intelligence would still reach the president aboard Air Force One through backup networks, and that Five Eyes intelligence sharing was not affected. The outage came while President Trump was in the Philippines, ahead of a trip to China on Wednesday, per the same report.
The AP and CNN place the NSANet outage in a week of unrelated-looking failures. Neither says they are connected, and CNN reported no indication that any of them was a cyberattack.
| Date | Incident |
|---|---|
| Friday, Nov. 13 | Nationwide FAA ground stop, traced to one router in Arkansas |
| Monday, Nov. 16 | Thousands of Chase customers report problems with online accounts |
| Tuesday, Nov. 17 | NSANet outage; separately, an Apple outage hits Apple Music, the App Store and AppleCare |
The Terminal covered the FAA case when the agency ruled out an attack before naming the router fault, and the trigger was still unknown: the FAA ground stop. The pattern there was the same as here. An early "not a cyberattack" came from officials before a technical cause was published.
What is not known
The NSA has not said which systems were under maintenance, who performed it, or why that maintenance degraded a network built with redundancy. Clayton's explanation, that organisations are patching and upgrading at the same time, covers the week's incidents in general and is not specific to NSANet. Warner's wording is conditional: "so far."
Maintenance is a plausible cause, and so is an unrelated fault. Without a published post-incident report, neither can be checked. The date to watch is the first NSA or Office of the Director of National Intelligence statement that gives a duration. For a different kind of failure where a vendor's notice named no flaw at all, see Optimizely's CDN serving a card skimmer.
Sources
More in Security
- 01Ruby2Shell (CVE-2026-132825): Ruby Is Fixed, but GitLab, GitHub Enterprise and Chatwoot Are Listed Without a PatchA one-byte heap overflow in Ruby's case conversion carries a 7.4 local score, while the researchers say stock Rails is remotely reachable and will publish a proof of concept Nov. 25.
- 02NPCI Wants Overlay Permissions Restricted on Sideloaded Apps; Google's 2024 India Block List Omits ThemThe reported ask covers accessibility, device admin and display-over-apps. The pilot Google announced on Oct. 3, 2024 named four other permissions.
- 03CVE-2026-99312: A KVM Nested-AMD Bug Scores 8.8, With Fixes Listed for Three Kernel BranchesThe Linux CNA's scoring notes describe a freed page-table root that a guest can aim at; the commit message describes only a stale MMU context.
- 04CISA's Nov. 18 KEV Additions Include Apache Axis 1.x, Which Has No Fix, With a Nov. 21 DeadlineThree of four new entries carry a three-day federal deadline; LiteLLM's advisory names two different patched versions.