iDirect Satellite Modem Flaw Skips Authentication Entirely
Security / news
iDirect Satellite Modem Flaw Skips Authentication Entirely
The pre-configured account CISA flagged needs no stolen password, and the iQ200 modem often serves as the only communications link to offshore rigs and vessels.

An attacker with local console access to an ST Engineering iDirect iQ200 satellite modem can escalate to full administrative control using an account the device ships with by default, no stolen password required. CISA disclosed the flaw, CVE-2026-38056, on Sept. 11 as part of an updated advisory for ST Engineering iDirect's iQ-Series terminals, rating it 9.4 out of 10 on the newer CVSS 4.0 severity scale.
Why the score does not overstate the risk
The device "ships from the factory with a pre-configured low-privilege local user account," CISA's advisory says, intended for field technicians who need shell access for maintenance but not full administrative control. "This built-in account provides the initial access required to exploit this vulnerability," the advisory says. "No additional credentials need to be obtained or brute-forced." The only precondition is physical or console access to the modem itself.
Three older flaws in the same advisory
CISA first published the advisory, tracked as ICSA-26-183-01, on July 10, disclosing two other bugs. CVE-2026-38059 lets an unauthenticated attacker with network access query the terminal's /api/identity endpoint and retrieve its serial number, Device ID and Terminal Private Key identifier, credentials the iDirect platform uses to authenticate a terminal to the satellite network. CISA said the exposure could enable terminal impersonation. CVE-2026-38057 is a cross-site request forgery bug: the /api/reboot endpoint accepts session cookies without the SameSite attribute, letting an attacker trigger repeated reboots. A fourth flaw, CVE-2026-38058, discloses information to anyone holding valid web credentials.
- CVE-2026-380569.4 score out of 10
- CVE-2026-380598.7 score out of 10
- CVE-2026-380588.6 score out of 10
- CVE-2026-380577 score out of 10
Source: NIST National Vulnerability Database, accessed 2026-09-12
Why a satellite modem gets this much scrutiny
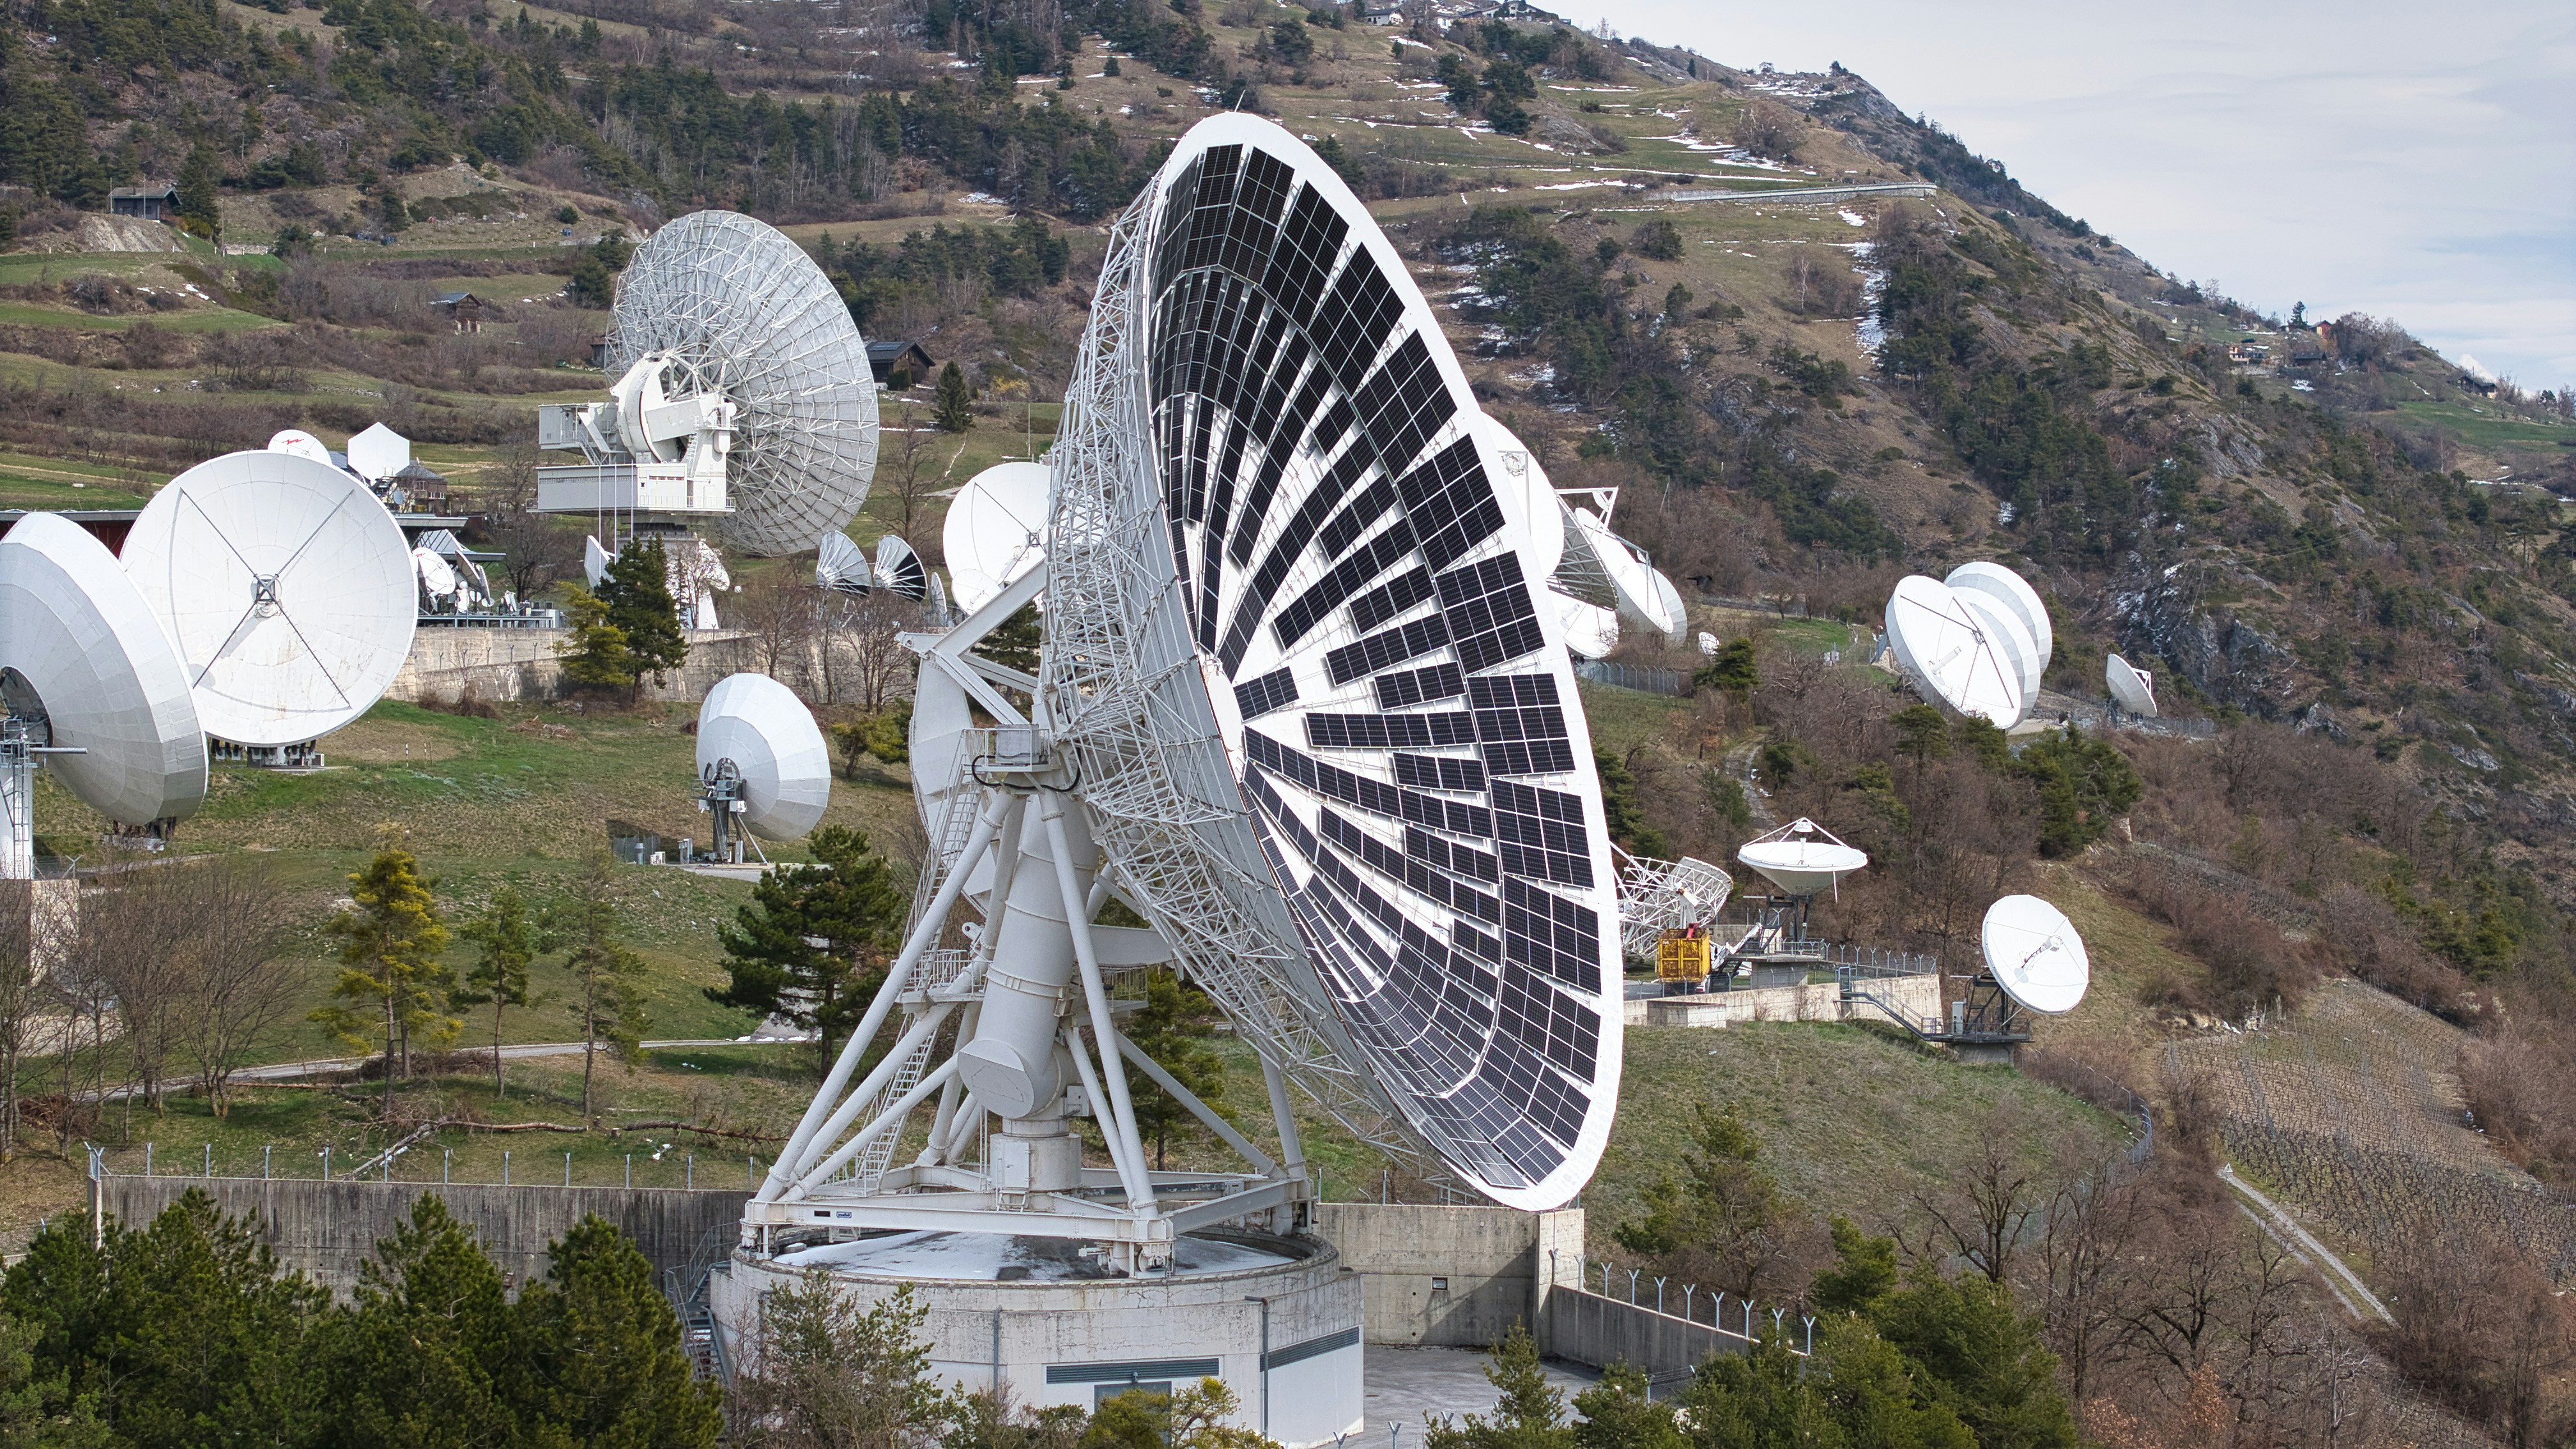
The iQ200 is a rackmount VSAT modem CISA describes as deployed across oil and gas, maritime, defense and remote infrastructure, often as the primary or only communications link for offshore rigs, vessels and remote sites. Ahmed Alqahtani of Aramco is credited with reporting the vulnerabilities to CISA.
What changed between July and September
The July 10 version of the advisory covered only CVE-2026-38059 and CVE-2026-38057. CISA's Sept. 10 revision, labeled Update A, added CVE-2026-38056 and CVE-2026-38058 and recalculated the CVSS 4.0 scores for all four. ST Engineering iDirect fixed every flaw in firmware version 4.5.3.0; every terminal running 4.5.2.1 or earlier remains exposed until an operator updates it through ST Engineering iDirect's own support portal. CISA has not said whether any of the four flaws has been exploited, and the advisory carries no indication that field technicians' pre-configured accounts have been changed as a companion fix. CISA has issued other industrial-control advisories in the same window, including one covering flaws in NextGen Healthcare's Mirth Connect integration engine.
The advisory follows a familiar pattern in CISA's industrial-control notices, including its earlier one on AVEVA's pipeline integrity software: equipment whose default configuration trusted a maintenance account more than it should have.
Sources
More in Security
- 01Go Team Weighs Turning Off Default MPTCP After Linux FlawThe Go Security Team called a default change premature on Oct. 29, while commenters on golang/go issue 82717 split over keeping multipath TCP on.
- 02Anthropic's Claude Exploit Chains Hit Five Targets, Each With LimitsThe Frontier Red Team's Oct. 27 post covers Chrome, Safari, Android, Windows and Linux, but only the Chrome and Linux results reach code execution.
- 03A Tampered Claude Code Extension Sat in Cursor's Marketplace for 11 Hours and Left an SSH Key BehindVersions 2.1.312 and 2.1.313 carried a 7,386-byte loader that plants an attacker key and a reverse tunnel. Uninstalling the extension does not remove either.
- 04Ivanti Connect Secure Zero-Day Chain Gave Root on a Patched VPN, and the Integrity Checker Misses ItVolexity dates exploitation to October 3, ten days before Ivanti's advisory; the root escalation step has no CVE and no fix in the sources reviewed.